FANMAP ADMIN — 2026 | Haru Li
The problem
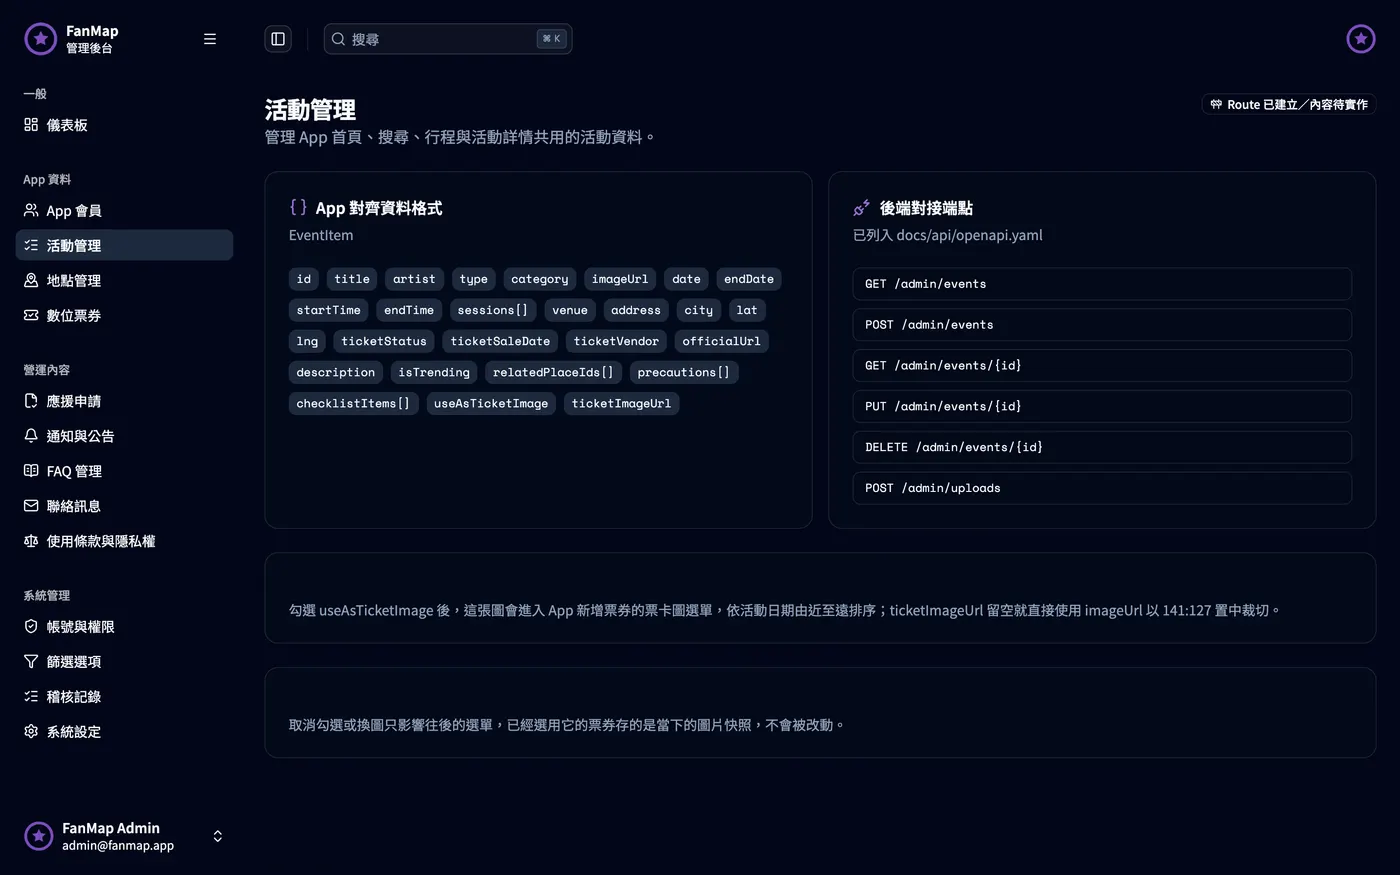
Everything the app shows — events, places, tickets, support applications — needs someone maintaining it, and the console's data model has to match the app exactly or the two ends grow separate formats.
Approach
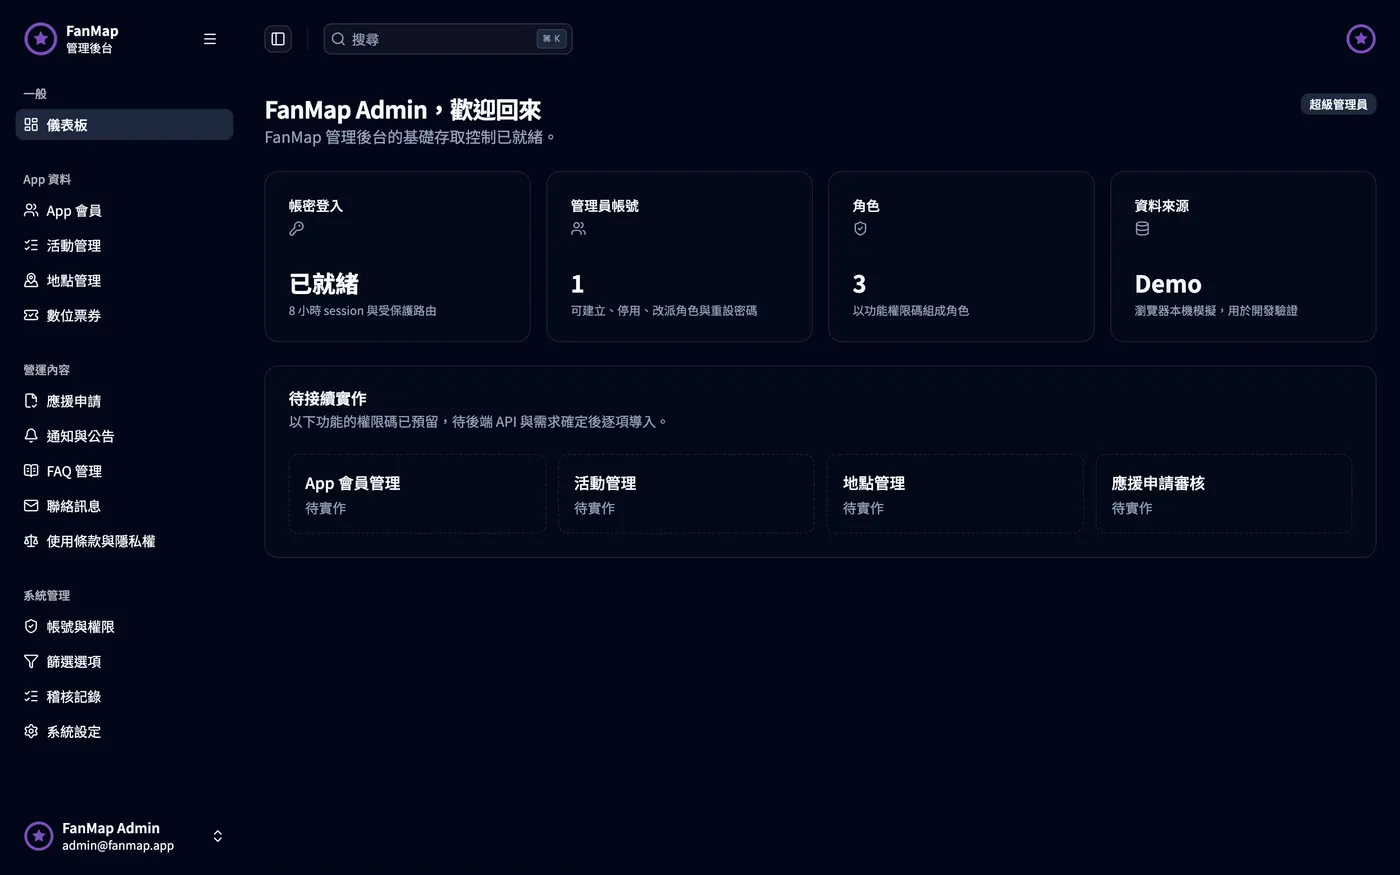
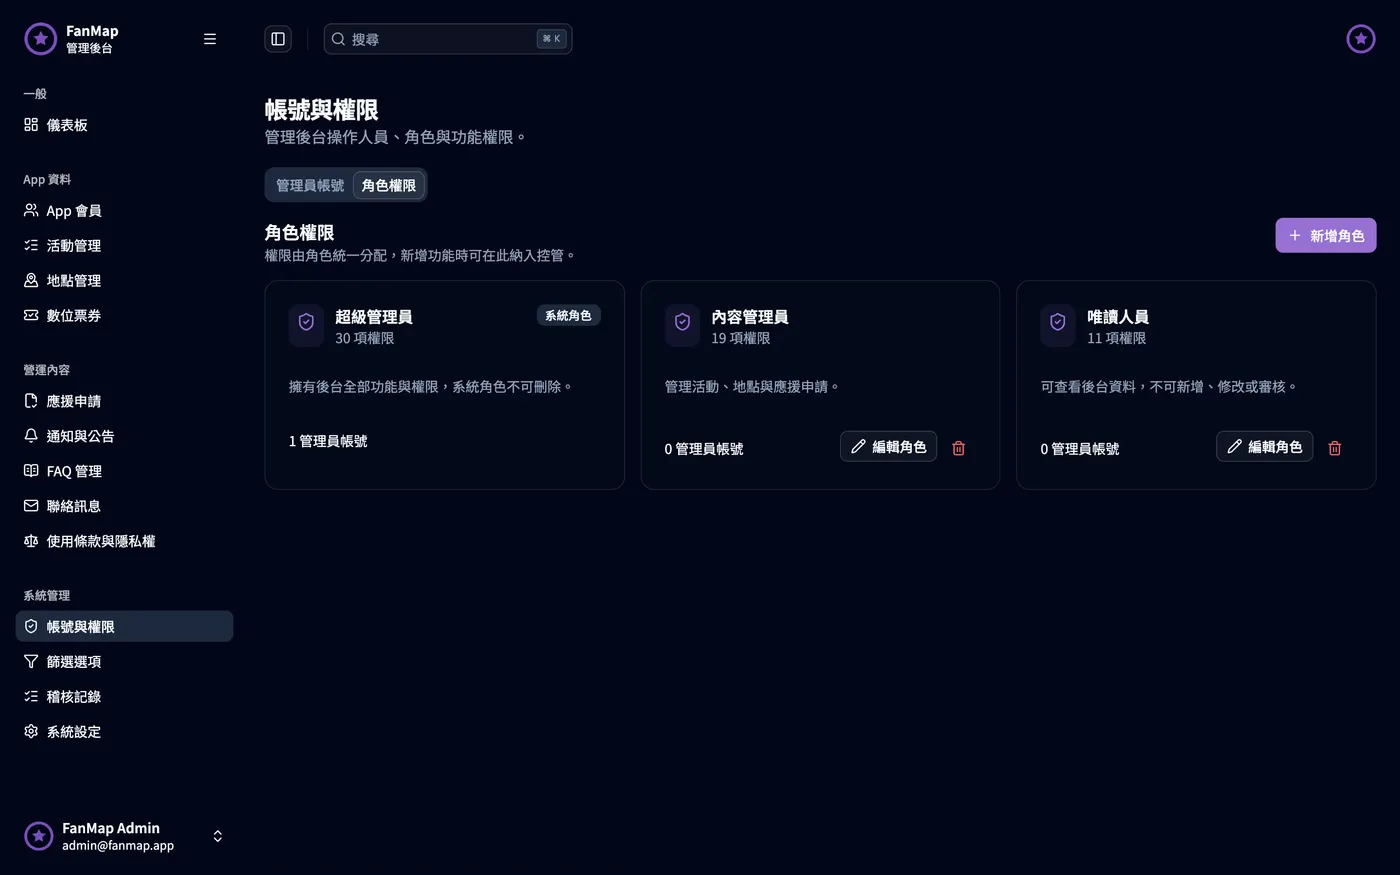
The admin console for the same team; I lead its frontend while the backend is built by other team members. Starting from an open-source Shadcn admin template, I rewrote the auth and permission layer: credential login, 8-hour sessions, protected routes, and admin accounts with roles and fine-grained permissions. It shares the app's core types for events, places, tickets and support applications rather than defining a second set. The contract with the backend was written in OpenAPI before either side built against it: admin endpoints all live under /admin/* behind JWT Bearer auth, and every operation declares the permission the backend must enforce — the frontend's route guards and hidden buttons are there for the experience, not the security. Legal documents keep draft and published versions apart so unfinished text never reaches the app. Tested with Vitest in browser mode.
Outcome
The foundation and the legal-document page are operational; the remaining 14 admin routes have their fields and API skeletons in place and ship page by page as the backend lands.